Set up the workspace
You created the workspace, so you are its owner and a kcap admin. Your first visit opens the setup wizard over the app, described below; Administration is in your avatar menu afterwards, and opens on General → Sessions. Nothing here needs to be done before people start storing sessions, but three things are worth doing on day one
1. Invite the first people
Section titled “1. Invite the first people”People → Invitations: an email address and a role, Member or, for owners, Admin. Kurrent emails a link valid for seven days; the person signs in through single sign-on and joins with that role. Invitations and active members both count against the plan’s seats. People, roles and teams
Point them at Join a kcap workspace; they do not need the URL
2. Decide the organisation’s default visibility
Section titled “2. Decide the organisation’s default visibility”Members’ sessions default to org_public, which means readable by the organisation for the organisation’s own repositories. Which repositories count is yours to set: General → Sessions → Org-visible sessions, a comma-separated list of GitHub organisation or user names. Blank uses the connected GitHub account. Without it, org_public sessions stay private. Sessions and repositories
3. Configure what AI is doing the work
Section titled “3. Configure what AI is doing the work”Titles, outcome summaries, embeddings and evaluations run on Kurrent-managed AI on every plan, with nothing to configure. Add your own provider keys under AI & models → AI Providers when you want a particular vendor or model, and decide whether sessions are evaluated automatically under Evals. AI providers and models
Optional, any time
Section titled “Optional, any time”- Teams, for sharing sessions with a named group. People, roles and teams
- Slack, for link previews and direct-message notifications; a wizard that takes about two minutes. Integrations
- The GitHub App, so pull-request and issue context reaches sessions and work items. Integrations
- The Linear app, so sessions link to the Linear issues they touch. Integrations
- Machine credentials, for CI runners. Store sessions from headless machines
- Projects, which members create themselves from the scope selector on Team and Enterprise plans
The setup wizard and Getting started
Section titled “The setup wizard and Getting started”From kcap 1.4, a new workspace’s admin lands in a setup wizard over the app: Install kcap on your machine, Invite your team, Connect GitHub, Connect Linear, Install the Slack app, then Start using kcap. A step already done, or not offered on your workspace, is left out, and anything Kurrent already manages for you is never a step. Skip and Next both move on and store nothing, so a skipped step stays open as a card on the Getting started page. GitHub, Linear and Slack open in another tab; when you come back, the wizard has re-read where you got to
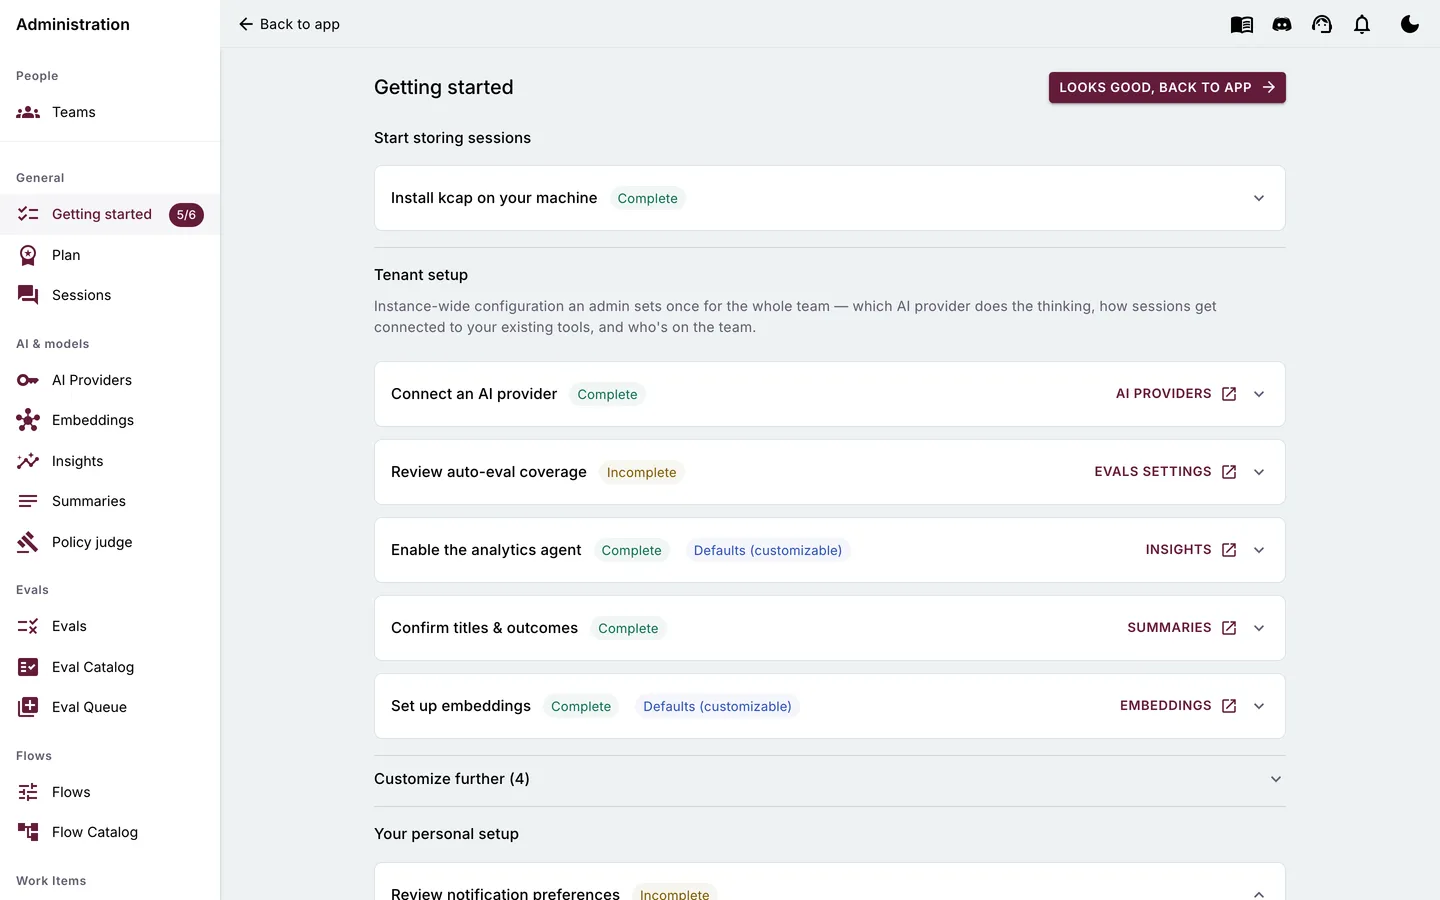
The same items live on as cards under General → Getting started (/admin/getting-started), where the admin nav shows a badge of how many required ones are still open. Tenant setup holds the required cards: Connect an AI provider, with Review auto-eval coverage, Enable the analytics agent and Confirm titles & outcomes under it; Set up embeddings; Invite your team. Customize further folds the optional ones away: the GitHub App or a GitHub token, Slack, the Linear app or a Linear token, and your first project. Each card carries a chip, Complete, Incomplete, Blocked while a step it depends on is open, Skipped, or Complete with Defaults (customizable) when Kurrent’s managed setting is in use; opening it shows what the item unlocks, what it needs, its action and Mark done, with a link to the settings page it concerns. The first card still to do opens by itself, so a returning admin lands on the next thing. Members have their own cards under Get set up in the avatar menu
Who can do what
Section titled “Who can do what”Owners and organisation admins manage members, invitations and the plan. The other console pages need kcap administrator access; on a shared deployment an organisation admin does not automatically have it. An owner can promote, demote and transfer ownership from Members. A locked-out workspace can be recovered by the operator with the deployment’s Auth:Admin:UserIds setting
Settings saved in the console are stored encrypted and take effect without a restart; a field supplied by the deployment’s environment is shown locked